Vort3x | Cybersalon | November 15, 2026
Vort3x | Cybersalon | November 15, 2026
Vort3x, published on the 15th of each month, aims to pick out significant developments in the intersection of computers, freedom, privacy, and security for friends near and far. The views expressed in these stories do not necessarily reflect those of Cybersalon, either individually or collectively.
Prepared by Wendy M. Grossman.
Contents: Cybersalon events | News | Features | Diary
Cybersalon Events
4th Dec Charity Hack Day
Newspeak House, London
Join us for the first Hack Day for the Charity/NGO sector!
For people who build, fund, run and use tech in charities
NEW JOBS in AI Security (London)
Research Scientist – Human Influence (deadline 29/11, London based)
Technical AI Research Manager (London)
Supporting work by AI Safety Teams in LISA /Arcadia labs
NEWS
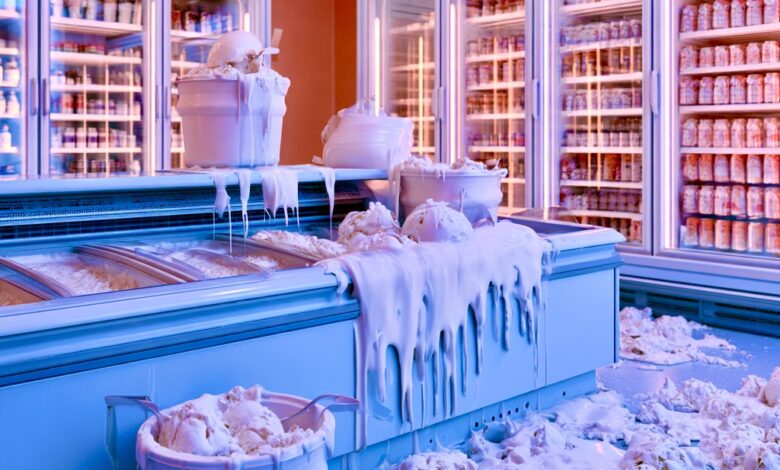
Hot Ice-Cream attack -how Hackers broke into Fridges
———————————————————————-
The October hacker attack on French supermarkets was due to poor security, Dan Goodin reports at Ars Technica. All three controller types reportedly hacked had critical vulnerabilities that allowed attackers to log in remotely with administrators’ system privileges. The access allowed them to raise the temperature as high as 50C, spoiling millions of euros worth of food. Among the vulnerabilities: the fridges’ firmware hadn’t been patched, remote access should have been inside a VPN, and the list of allowed IP addresses should have been specified. Nadia Dubois reports at Tech Insider that two weeks later, a similar attach was made on three French blood bank freezers. Fortunately, the attack was caught quickly and no blood products were spoiled.
Comment: Many have wondered since why fridges are designed to heat up to 50C and why they would be connected to the Internet. We learned that the heat is necessary for defrosting, and remote control is needed for monitoring and quick response – though as Goodin says it must be carefully secured.
Amodei siblings to strike gold as Anthropic Files for IPO
———————————————————————
Anthropic has filed its S-1 prospectus with the Securities and Exchange Commission in preparation for its IPO, Robert Hart reports at The Verge. Among the more unusual elements in its 300 pages, Hart finds that co-founder siblings Dario Amodei and Daniela Amodei are jointly paid compensation of more than $34 million; risk factors include AI systems’ potential to cause catastrophic harm; it has billions of dollars in commitments for computational power; its seven co-founders will control 50.1% of shareholder voting power; and it claims its only rivals are OpenAI and Google. At Apollo, Torsten Slok reports that AI technology has to date delivered no financial payoff at all to American corporations outside of the technology industry. At The Register, Simon Sharwood reports that in announcing its quarterly results Alphabet has admitted that today’s AI mode searches bring in less revenue for Google, which is nonetheless spending enormous sums on infrastructure. At Gizmodo, Tom McKay reports that many US banks are blocking AI agents from moving money on the grounds that the technology introduces too much risk.
Phishing Attack on Binance Months in the making and Nets $6.3 billion
———————————————————————-
Hackers used fake job interviews, malware, and compromised internal AI tools over a period of months to break into the cryptocurrency exchange Binance and stole $6.3 billion in cryptocurrencies, Tanaya Machel reports at CNBC, based on an interview with co-CEO Richard Teng. The company has replenished 98% of the affected assets. The FBI has linked the attack to North Korean attackers.
France Proposes Per-Gigabyte Data Tax
———————————————————————-
French lawmakers have approved a proposal, which must still pass the Senate, to tax Internet data by the gigabyte, Newton Gitonga reports at Tom’s Hardware. The proposers claim the tax could generate around €10 billion a year for the government, which they expect will be paid by content providers. Explanatory notes indicate that they are focused on Google, Meta, Netflix, Amazon, and content delivery network Akamai, which jointly account for about half of French Internet traffic; TikTok and other such platforms could also come within the proposal, depending on how the rules are applied. Opponents argue that the tax will be passed on to consumers pushing inflation up.
Unsafe Ads Spread Spyware
———————————————————————-
Targeted ads can be used to deliver zero-click mercenary spyware using a technique called AdFection, which was used to infect devices at Al Jazeera with spyware from Candaru, Citizen Lab reports. The malicious ads were bought by the Israeli company Discover-Tech, which facilitates multiple spyware partners, via its Controlium platform. In its analysis of four billion Discover-Tech bidding records, the lab found that over a period of four months the company’s ads were shown on almost 200,000 unique websites and Android/iOS apps in dozens of countries. Citizen Lab calls on regulators to investigate.
FEATURES & ANALYSIS
Ofcom Reports Online Safety Act Has Changed Little
———————————————————————-
In its first required progress report since the Online Safety Act came into force, Ofcom admits the law has had little effect in preventing minors from accessing harmful material, Robert Booth reports at the Guardian. The sole exception is access to commercial pornographic websites, which operate age verification. Children report that they encounter pornographic content most often via personalized feeds. An Ofcom spokesperson said nonetheless that “significant progress is being made”. Ofcom recommends that body stigma and depression should be moved into the category of priority content.
UK Embeds AI Throughout Digital Hostile Environment
————————————————————–
In a new report, the Open Rights group examines the “digital hostile environment” that sees AI being embedded throughout the immigration system and at the UK’s borders in “near total secrecy” and “reinforcing bias and discrimination”. Technological change also includes a shift from reactive to proactive immigration enforcement.
Comment: Governments easily get away with expanding surveillance in immigration enforcement because the general population is rarely aware of it and immigrants can’t vote. But migrants are often the test group for new technologies that then spread across to the rest of us.
Replacing the Turing Test
————————————————————–
In this article at The Skeptic, Richard Glover argues that we need to replace the Turing test with a new way of measuring intelligence and proposes splitting it into separate tests for verbal, emotional, and social elements. Even within those, further distinctions are necessary, for example the difference between expressive and receptive verbal intelligence. At the Mystery AI Hype Theater 3000 newsletter, Emily Bender and Nanna Inie offer replacements for common terms such as “artificial intelligence” (“probabilistic automation”), “hallucinations” (“undesirable outputs”) and “speech recognition” (automatic transcription”) to avoid anthropomorphizing technologies.
Canada Wants Law Enforcement Access to Encrypted Data
——————————————————————–
In their Kernel Panic newsletter at Wired, Lily Hay Newman and Matt Burgess discuss Canada’s C-22 bill, which would allow the government to require technology companies, even when they’re outside Canada, to provide “technical capabilities” so that law enforcement can access data as well as retain user metadata. The move matches similar proposals over the years in the US, UK, and other countries even though cryptographers, security experts, and even governments’ own security services continue to warn that building in backdoors, vulnerabilities, and intentional flaws in encryption cannot be done safely. Members of the US House Judiciary and Foreign Affairs committee wrote in May to Canadian officials opposing the plan. Apple and Meta have criticized the bill, and Signal says it will exit the Canadian market if the measure passes.
Comment: As Newman and Burgess say, these proposals keep popping up all over the world. The require to retain user metadata is particularly problematic for services like Signal and many VPNs, whose infrastructure is explicitly designed not to do this. The recent attacks on fridges and blood banks ought to make it clear how risky this kind of thing is.
Bankruptcy Threatens Privacy of Chatbot Data
——————————————————————–
At Techdirt, Caroline De Cock outlines the threat to privacy raised when AI companies go bankrupt, are sold, or are tangled in legislation, in particular Character.ai, which filed for Chapter 11 on October 12 and its trying to sell its business, and rulings in New York Times v. OpenAI that has required OpenAI to retain logs of user chats that would otherwise have been deleted. De Cock compares the chat logs to personal diaries written on pages that belong to third parties – and yet they become business assets. She ends by suggesting four rules to prevent these “diaries” from becoming auction lots.
DIARY
—————————————-
December 14-18, 2026
Nairobi, Kenya
The 21st annual meeting of the Internet Governance Forum, which serves to bring people together from various stakeholder groups in discussions on digital public policy, is expected to draw more than 9,000 participants from 165 countries to contribute their perspectives on the most pressing issues, priorities, and challenges in the governance of digital technologies.
—————————————-
December 27-30, 2026
Hamburg, Germany
Over the last 40 years, the Chaos Communication Congress has become a Europe-wide renowned event with more than 17,000 participants annually, drawing an ever-growing group of international guests.
—————————————-
February 9, 2027
Washington, DC, and online
Hosted by the Internet Education Foundation and annually attracting over 600 attendees, the State of the Net Conference provides unparalleled opportunities to network and engage on key policy issues. It is also the only Internet policy conference with over 50 percent of Congressional staff and government policymakers in attendance, making it the perfect setting to explore important, emerging trends.
—————————————-
February 9-10, 2027
London, UK
The 2027 State of Open Con will focus on Open Technology including open source software, open hardware, open data, open innovation, open standards, and the value that the open community brings to the UK and its digital economy. Alongside a diverse range of topics, the event promises to include a diverse range of speakers and participants.
Computers, Privacy, and Data Protection
—————————————-
March 8-11, 2027
CPDP offers the cutting edge in legal, regulatory, academic and technological development in privacy and data protection, gathering cademics, lawyers, practitioners, policy-makers, industry and civil society from all over the world. Held annually in Brussels, CPDP offers an arena to exchange ideas and discuss the latest emerging issues and trends. This unique multidisciplinary formula has served to make CPDP one of the leading data protection and privacy conferences in Europe and around the world.
—————————————-
April 22-24, 2027
Oxford, UK
We Robot 2027 is an international platform to discuss current and future robotics and AI policy. We bring together academics, policymakers, business leaders and the broader expert community to discuss shared strategies for managing the rapid advancements in robotics and AI. As the 15th annual conference, We Robot 2027 will be hosted by the Institute for Ethics in AI at the University of Oxford.
—————————————-
April 26-30, 2027
Venice, Italy
The Venice Privacy Symposium aims to promote international dialogue, cooperation and knowledge sharing on data regulation, compliance, and innovative technologies and to present top level experts shedding light on the latest developments in data governance, regulatory compliance and innovative technologies.
—————————————-
June 3-4, 2027
Atlanta, Georgia
PLSC is the world’s premier academic conference of privacy, law, and technology scholars, researchers, and practitioners. We incubate and critique scholarship at the vanguard of the field of law and technology. There will be a mentorship pre-conference on June 2.
—————————————-
July 20-22, 2027
San Francisco, CA, USA
As the only global conference dedicated to the work of trust and safety professionals, TrustCon is where practitioners explore the most challenging issues facing the field in a collaborative, open, and welcoming environment. Attendees of TrustCon are trust and safety experts from industry, civil society, researchers, and government, who come together with the goal of knowledge building and connecting.
